This product was not featured by Product Hunt yet. It will not be visible on their landing page and won't be ranked (cannot win product of the day regardless of upvotes).
Product upvotes vs the next 3
Waiting for data. Loading
Product comments vs the next 3
Waiting for data. Loading
Product upvote speed vs the next 3
Waiting for data. Loading
Product upvotes and comments
Waiting for data. Loading
Product vs the next 3
Loading
Preflight: MCP server security check
Check an MCP server for auth gaps before you connect
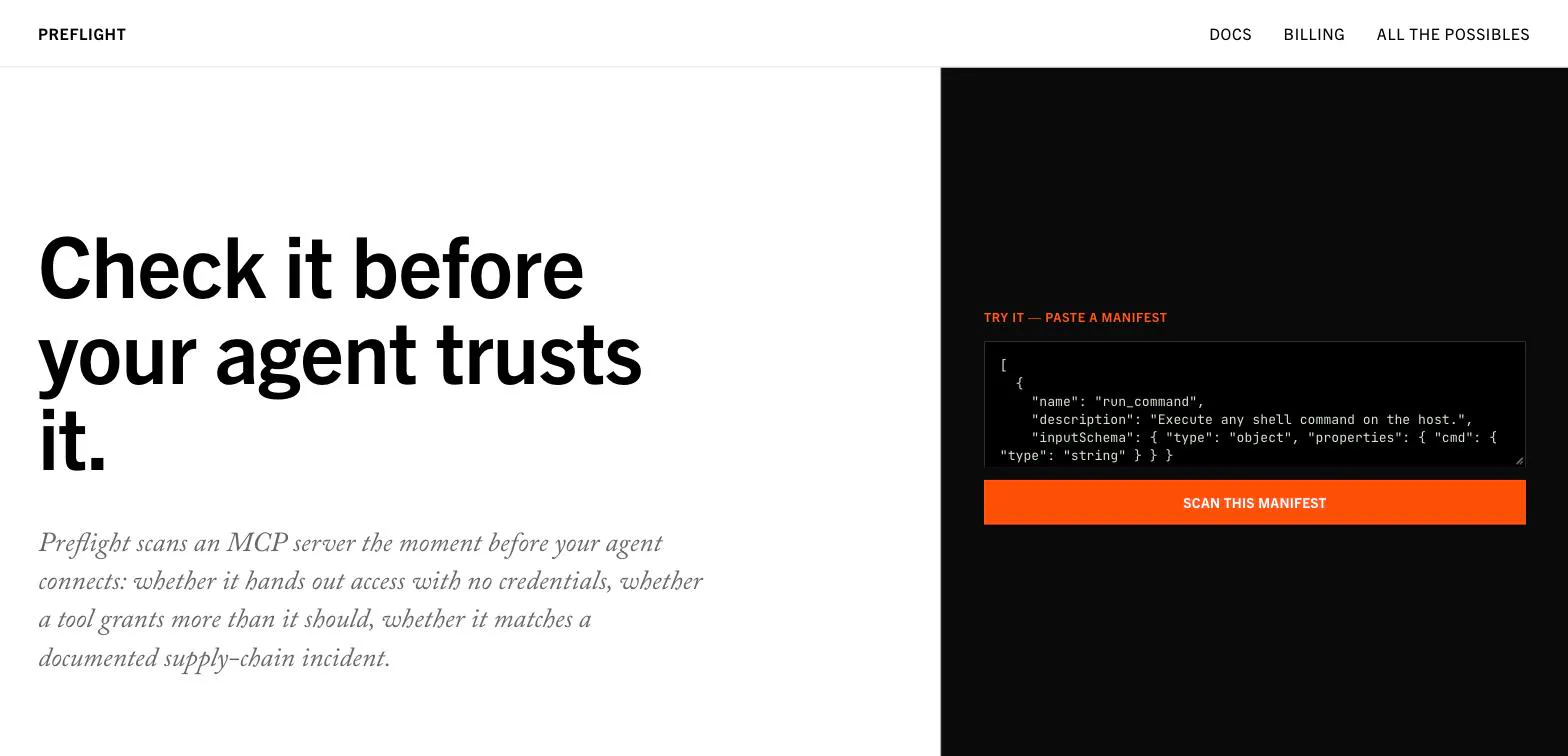
Preflight checks an MCP server for real security gaps before your agent connects: unauthenticated transport, capability grants with no scoping, known-bad description signatures, and a semantic pass reading tool descriptions for injected instructions aimed at the model. Free tier is real: 20 scans/minute, no signup. Tested against real production servers (Linear, Sentry, Atlassian) so it doesn't cry wolf on things already secured properly. Built by All the Possibles.
I kept seeing the same pattern: someone finds an MCP server on a registry, wires it into their agent, and only later notices it hands over a full tool list with zero auth, or grants shell/credential access with no scoping. Nobody actually reads a tool's description before granting it access, the same blind spot as clicking through a permissions dialog.
Built Preflight to check before connecting. It flags unauthenticated transport, unscoped capability grants, known-bad description signatures, and a semantic pass reading tool descriptions for injected instructions aimed at the model. Free tier is real, 20 scans/minute, no signup, MCP server or plain REST API.
Would genuinely like to hear about false positives or negatives if anyone tries it against their own servers.
About Preflight: MCP server security check on Product Hunt
“Check an MCP server for auth gaps before you connect”
Preflight: MCP server security check was submitted on Product Hunt and earned 0 upvotes and 1 comments, placing #9 on the daily leaderboard. Preflight checks an MCP server for real security gaps before your agent connects: unauthenticated transport, capability grants with no scoping, known-bad description signatures, and a semantic pass reading tool descriptions for injected instructions aimed at the model. Free tier is real: 20 scans/minute, no signup. Tested against real production servers (Linear, Sentry, Atlassian) so it doesn't cry wolf on things already secured properly. Built by All the Possibles.
On the analytics side, Preflight: MCP server security check competes within Developer Tools and Security — topics that collectively have 522.7k followers on Product Hunt. The dashboard above tracks how Preflight: MCP server security check performed against the three products that launched closest to it on the same day.
Who hunted Preflight: MCP server security check?
Preflight: MCP server security check was hunted by All The Possibles. A “hunter” on Product Hunt is the community member who submits a product to the platform — uploading the images, the link, and tagging the makers behind it. Hunters typically write the first comment explaining why a product is worth attention, and their followers are notified the moment they post. Around 79% of featured launches on Product Hunt are self-hunted by their makers, but a well-known hunter still acts as a signal of quality to the rest of the community. See the full all-time top hunters leaderboard to discover who is shaping the Product Hunt ecosystem.
For a complete overview of Preflight: MCP server security check including community comment highlights and product details, visit the product overview.

 All The Possibles